SafeNet MobilePASS+ is a Mobile & Desktop Authenticator App for Push and OTP Authentication
SafeNet MobilePASS+ is a next generation authenticator app that offers secure one-time passcode (OTP) generation on mobile, wearables and windows devices, as well as single-tap push authentication for enhanced user convenience.
SafeNet MobilePASS+ authenticator has been designed to provide unmatched security on multiple supported platforms (Android, iOS and Apple Watch, Chrome OS, Windows 10 and 11) with the best-in-class native end-user experience.
4.5 Rating
Google Play, App Store & Microsoft Store
30,000
organizations worldwide trust us
3 years
KuppingerCole Leadership Compass leader for Passwordless authentication
Why it matters
Identity is the new perimeter
Identity threats are rising, compliance is tightening, and too much friction creates risky workarounds.

Rising identity threats
Phishing attacks account for one third of all data breaches, and not all MFA prevents it.
Increasing compliance pressure
Regulators are raising expectations for MFA adoption for all users—not just highly privileged ones.
MFA friction drives risky workarounds
When MFA gets in the way, users work around it by reusing credentials. MFA adoption comes from frictionless solutions.
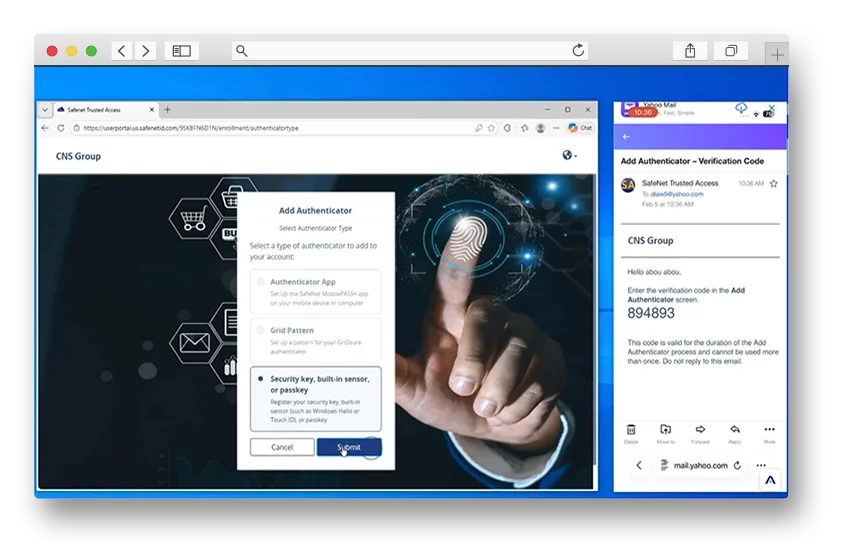
One mobile app. Every authentication journey.
MobilePASS+ is Thales’ mobile authenticator app—now equipped with FIDO2 device-bound passkeys that let users securely access their applications using a biometric like a fingerprint or facial recognition, all from their own mobile device.
Phishing-resistant, passwordless, high-assurance authentication
Uses biometrics (Face ID, Touch ID, fingerprint) already on the device
Turns the phone users already carry into a secure authenticator
Centrally managed security keys from the mobile device
Features & Capabilities
Everything you need, built in
From push and OTP to FIDO2 device-bound passkeys — MobilePASS+ supports the full range of MFA methods your access needs, in one app.
Device-Bound Passkeys
Security keys live only on the trusted mobile device, making them a stronger, phishing-resistant alternative to synced passkeys.
Biometric Authentication
Users authenticate with fingerprint or facial recognition — no passwords, no codes.
Push Authentication
Approve or deny login requests with a single tap.
One-Time Passcodes (OTP)
Generate OTPs on-device, even without an internet connection.
Centralized Management
Provision, monitor, and revoke authenticators at scale from a single admin console. Integrates natively with SafeNet Trusted Access and OneWelcome Identity Platform to enforce policy-based access across your internal and external identities.
Cross-Platform & Legacy-Ready
Available on iOS, Android, Windows, and macOS. Extend modern FIDO authentication to legacy resources through ADFS and RADIUS integrations.
4.5

Highly rated across Google Play, App Store, and Microsoft Store.
Fits into your existing identity stack
Integrates with the identity and access platforms you already use.
Related solutions
SafeNet Trusted Access
Cloud-based access management and single sign-on for the modern workforce.
Hardware Authenticators
FIDO and PKI security keys and OTP tokens for high-assurance use cases.
OneWelcome Identity Platform
Orchestrate secure, passwordless identity journeys for workforce, customers, and partners.
See how MobilePASS+ works at scale
Deploying phishing-resistant MFA to thousands of employees? See how organizations roll out MobilePASS+ with SafeNet Trusted Access for centralized policy, provisioning, and lifecycle management.
Related resources
Frequently asked questions
MobilePASS+ is Thales's mobile authenticator app that lets users securely access cloud, on-premises, web, VPN, and enterprise applications using push authentication, one-time passcodes (OTP), or FIDO2 device-bound passkeys — from a device they already carry.
Device-bound passkeys are FIDO2 credentials cryptographically tied to a single trusted device. They can't be copied, exported, or synchronized to other devices or cloud accounts — making them phishing-resistant and suited for high-assurance use cases.
Synced passkeys are replicated across a user's devices through consumer cloud ecosystems (e.g., iCloud Keychain, Google Password Manager), which is convenient but expands the attack surface. Device-bound passkeys stay on one device and require a biometric to use, offering stronger assurance for workforce scenarios.
Yes. When used with FIDO2 device-bound passkeys, MobilePASS+ delivers phishing-resistant, passwordless authentication that defends against credential theft, adversary-in-the-middle attacks, and MFA prompt-bombing.
Yes. If push notifications can't be delivered, users can manually generate a one-time passcode in the app and enter it to authenticate.
Administrators can revoke the lost device's authenticator centrally from the SafeNet Trusted Access console, and users can enroll a new device via self-service. Because device-bound passkeys are cryptographically tied to the lost device, they can't be reused by anyone else.
iOS, Android, Windows 10/11, macOS, Chrome OS, and Apple Watch.
MobilePASS+ helps organizations meet phishing-resistant MFA requirements in frameworks such as PCI DSS, NIS 2, and ISO 27001 by implementing FIDO2-based authentication. It is also FIPS 140-3 compliant as of the January 2026 release.