What is FIDO2?
FIDO (Fast Identity Online) is the umbrella term for FIDO Alliance's newest set of specifications.
Passkeys – based on FIDO2 technology - enable users to authenticate quickly and securely to online services without using password anymore.
Passkeys & FIDO2 authentication is the industry's future proof solution to the global password challenge and addresses all the concerns of traditional authentication, by providing phishing-resistant authentication combined with enhanced user experience in both desktop and mobile environments.
67 %
of organizations report an increase in credential theft and misappropriated secrets. Phishing has emerged as the #2 most common cyberattack affecting organizations worldwide.
Traditional passwords and MFA are no longer sufficient.
Source: Thales Data Threat Report
Thales FIDO2 security keys benefits
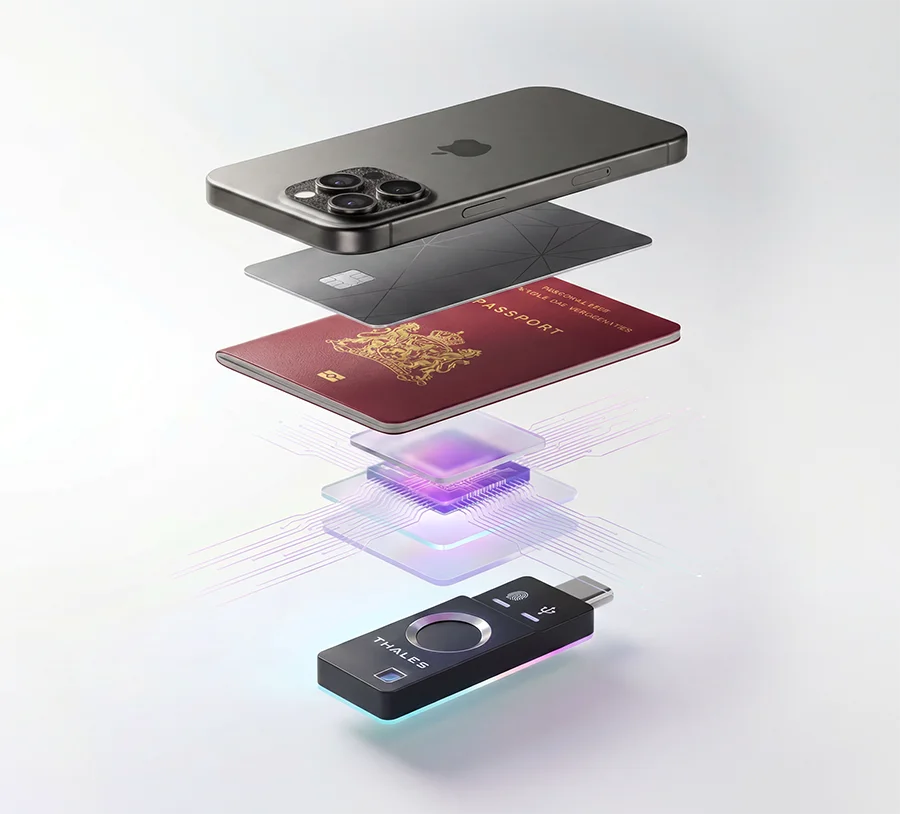
Thales multi-factor authentication devices use current and emerging protocols to support multiple applications at the same time. Use one security key that combines FIDO2, WebAuthn, U2F, and PKI to access both physical spaces and logical resources.
The right key for every user
Choose the form factors that fit how your teams work - whether they are on mobile, laptops, shared desktops, or in air-gapped environments.
With a single key, seamlessly combine physical access with digital access to both modern cloud and legacy resources.
Decades of technology innovation, built into every key
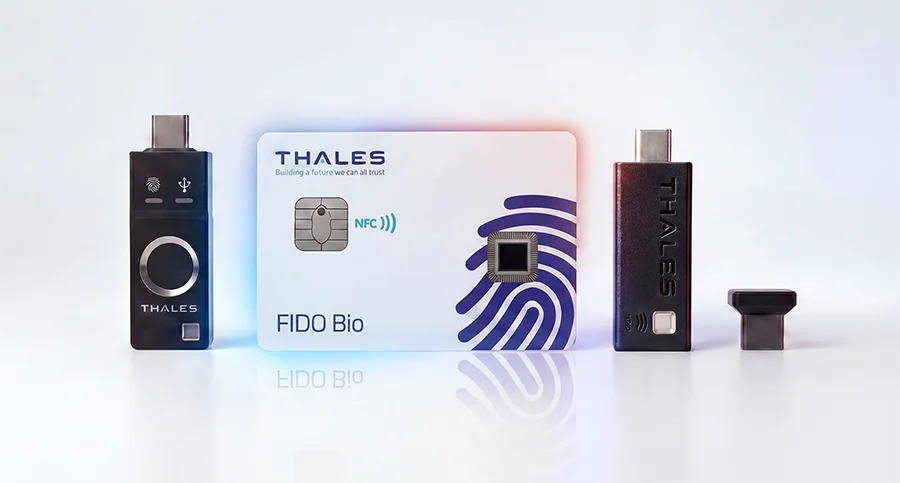
Phishing resistance is just the starting point. Thales backs every key with over 40 years of enterprise cybersecurity expertise, security-by-design engineering, and highly secure global supply chain, from manufacturing to delivery.
Roll out at scale without hassle
End users receive FIDO keys ready to use. This reduces setup errors and simplifies onboarding, allowing you to deploy phishing-resistant MFA across global teams in days.
Full lifecycle control
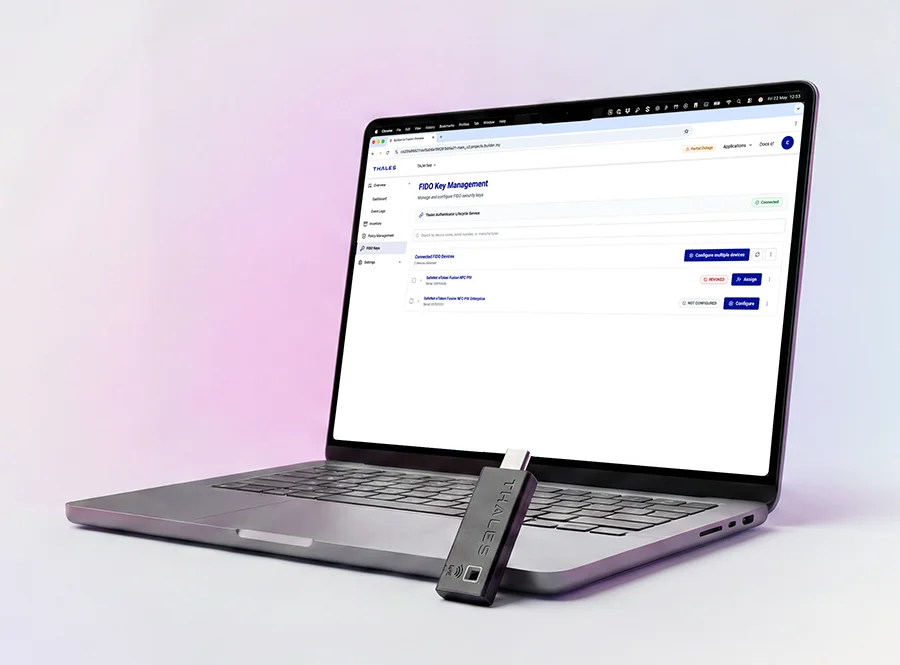
Manage FIDO keys throughout their life cycle, from activation to revocation, thanks to Thales Authenticator Manager Suite, management tools that let you configure, register, unlock and revoke keys instantly.
Eliminate the overhead of managing a physical fleet at scale and ensure the right key is used by the right user to access the right data.
Security that carries your brand
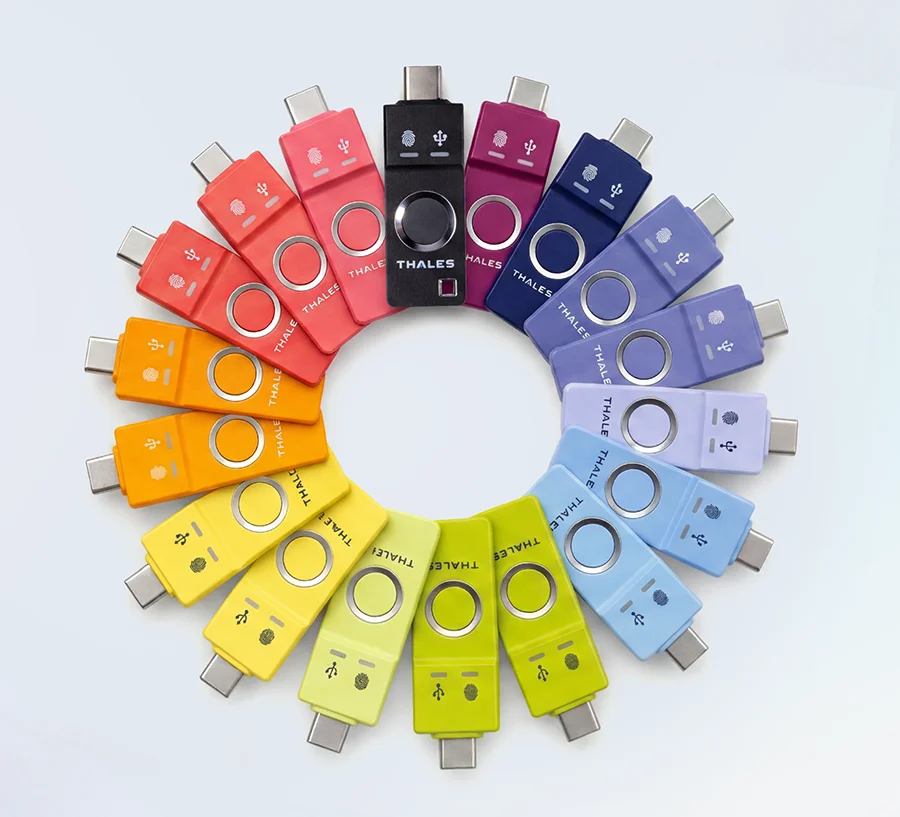
Reinforce organisational trust from day one. Deliver custom-branded security keys and packaging that match your corporate identity, improve user adoption, and make secure authentication feel like a native part of your workspace experience.
Sustainability without compromise
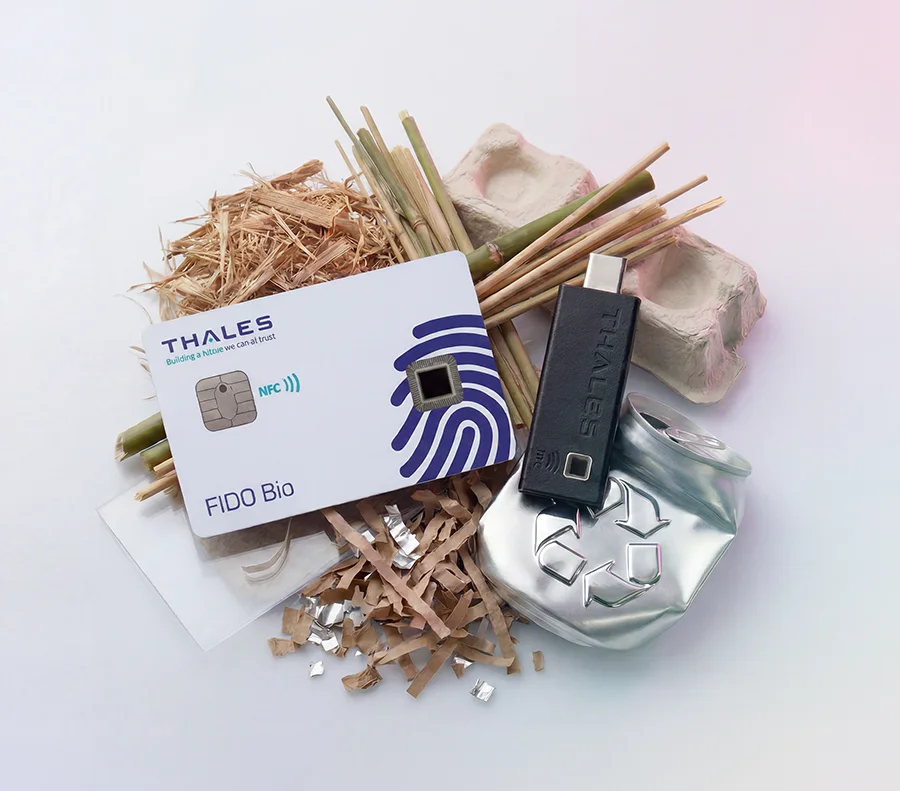
Protect your data while protecting the planet. Directly support your corporate ESG goals with security keys delivered in plastic-free packaging and lower impact material.
Meet global compliance standards with certified keys
Find the right FIDO2 security key that fits your needs
Thales supports numerous passwordless authentication journeys with a wide range of FIDO authenticators.
Go passwordless with SafeNet eToken FIDO series
Compact, tamper-evident USB tokens supporting FIDO2, available in USB Type-A, USB Type-C, and optional NFC models. Ideal for organizations replacing passwords with FIDO-based authentication across web applications, network domains, and shared-device environments.
Extend modern FIDO authentication to PKI use cases with SafeNet eToken Fusion series
Support both FIDO and PKI-based authentication for modern and legacy applications, network domains, digital signatures, and file encryption. NFC support enables use across multiple device types, while certifications help organizations address regulatory requirements.
Extend modern FIDO authentication to PKI use cases with SafeNet IDPrime FIDO Smart Cards
Support both FIDO and PKI use cases for secure access to modern and legacy applications, network domains, digital signatures, and file encryption. NFC support enables use across desktops and tablets, with certifications that help meet regulatory requirements.
Combine digital access with physical access with SafeNet IDPrime FIDO Smart Cards series
Thales offers organizations smart cards combining physical access with digital PKI/FIDO authentication. Converged Badge is an ideal solution for organizations who need to protect access to secure areas and sensitive digital resources. Reduce the cost of badge deployment and fleet management while increasing employee adoption.
Boost FIDO adoption with biometric authentication
Enable users to authenticate securely and easily across devices using a fingerprint instead of a password or PIN. Choose from biometric smart card and USB token options designed to simplify the user experience while strengthening phishing-resistant authentication.
Simplify FIDO Deployment at Enterprise Scale
With Thales Enterprise Edition security keys in combination with dedicated management tools, Thales allow organizations to manage their FIDO keys securely and easily throughout their life cycle. They add an administration layer and configuration policies to help IT teams deploy, administer, and support the end user.
Manage your FIDO keys throughout their lifecycle
While the FIDO standard delivers strong authentication, enterprises also require centralized lifecycle management, policy enforcement, and operational control. The Thales Authenticator Manager Suite helps organizations deploy, manage, unlock, and revoke FIDO credentials across the enterprise.
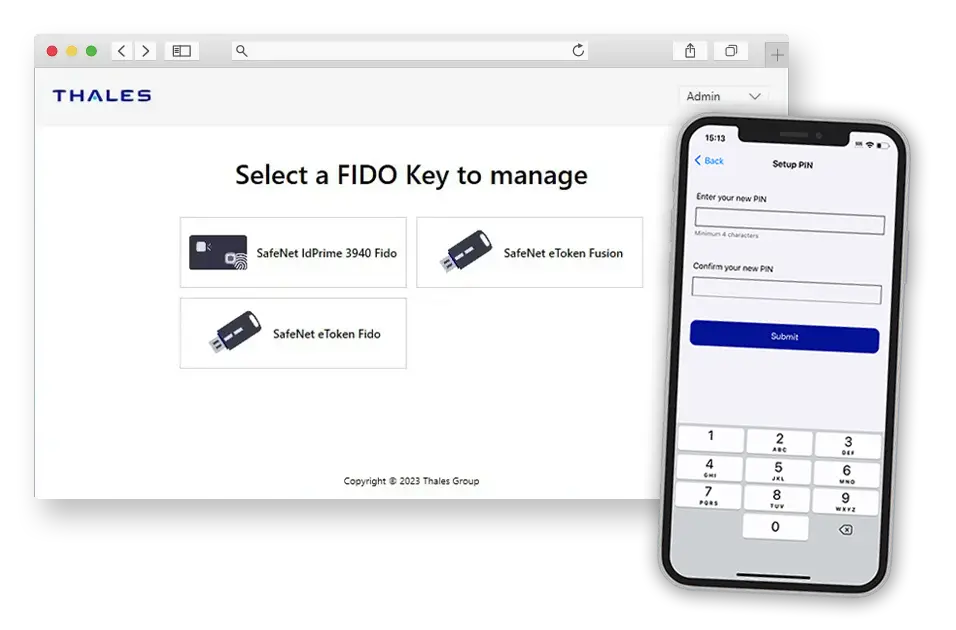
SafeNet FIDO key manager
Ideal for decentralized small- and mid-sized deployments, enabling users and administrators to manage FIDO credentials with ease.
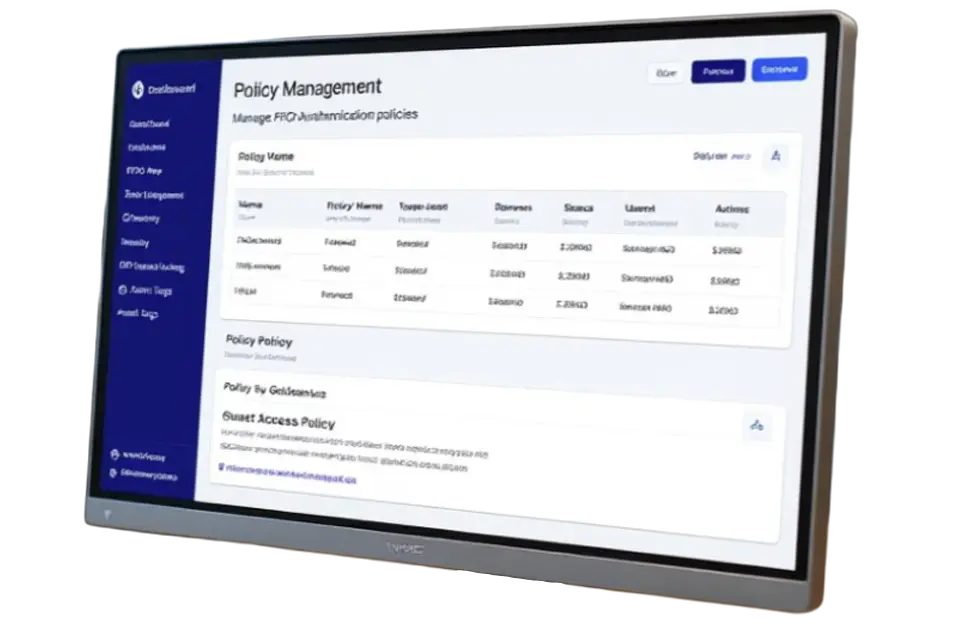
Thales authenticator lifecycle manager
Designed for large-scale, centralized deployments that require enterprise-wide visibility and control.
Secure access to Microsoft 365 and Windows devices
Thales and Microsoft partner to provide Microsoft 365 customers with FIDO and certificates-based authentication (CBA).
With the Entra ID, Microsoft customers can use Thales X.509 certificate-based Tokens, Smart cards, and FIDO authenticators for all their identity protection needs.
We chose Thales for their long-standing experience in strong authentication as well as for the richness of their authentication key management tools.”
Recommended resources
To select the key that fits your needs, consider the devices used and their connection modes (contact, contactless), the operations run (signature, physical or digital access) and the way to authenticate (PIN or biometrics). Questions you need to answer:
- Are the devices equipped with USB ports or card readers? Do they support wireless NFC?
- Do all the accessed digital resources support FIDO? If not, do they support PKI certificate-based authentication?
- Do my end users need to sign digital documents, encrypt sensitive emails or files?
- Do my end users access secured areas that require physical access control?
- Should we consider offering usage of biometrics instead of a PIN to simplify the end user’s experience?
It is a USB or smart card companion device that you can use to securely access sensitive online services without using a password. It uses the FIDO2 (Fast identity Online) standard developed by the FIDO Alliance.
The FIDO (Fast identity Online) protocol requires a “user gesture” (touch or tap the token) and/or a user verification (via a PIN or biometric) before the private key can be used to sign a response to an authentication challenge.
To access an online service, you just need to follow the online guideline displayed on the user interface: when requested, plug the token into the USB port of your device touch the sensitive sensor to confirm your presence, enter your PIn and you are logged in. Alternatively, if you use contactless and biometric token such as the SafeNet FIDO Bio Smart Card, you just tap the card on your device while putting your finger on the biometric sensor and you are in!
In FIDO2, passkeys are password replacements that provide faster, more accessible, and more secure sign-ins to websites and apps. They are resistant to phishing and credential stuffing, and designed so that there are no shared secrets.
There are two types of passkeys: synced passkeys (can be exported via a cloud service to another device) and device-bound passkeys (stored in a single device and cannot be copied). FIDO2 security keys/ tokens are device-bound passkeys.
Yes, FIDO2 tokens can be used with any mobile device, but depending on the connector of the token (USB-C or USB-A), the user may need to use an adaptor. If the token and the device are compatible with NFC, the user can also use the NFC capability directly by tapping the token to the back of its mobile device.
The Thales FIDO2 token is ready to use and requires no software or driver installation. You can set up your FIDO2 token by registering it to an online service. Set-up instructions may differ from one service provider to another, so follow the instructions displayed on the user interface. Generally, the service provider asks you to define your login name, a PIN code and put a name to the registered FIDO2 Token. Alternatively, you can use SafeNet FIDO Key Manager to set up and change the PIN of your Thales FIDO2 Token.
To learn more about this topic consult our dedicated section
FIDO2 tokens are compatible with all online services that support the FIDO2 standard.
You can look at our page of FIDO compatible services for more information.
There are different benefits of using FIDO2 passkeys over traditional passwords:
- Security: unique login credentials across every website which are never stored on a server, eliminating the risk of phishing and other forms of attacks.
- User experience: user login with simple built-in methods on the device or by leveraging easy-to-use FIDO2 security keys.
- Privacy: unique keys for each internet site that cannot be used to track users across sites. Biometric data, when used, never leaves the user’s device.
- Scalability: enable FIDO2 through simple API calls supported across all leading browsers and platforms.
Based on cryptography, FIDO2 authentication is recognized by cybersecurity agencies around the world as one of the most secure authentication methods. A FIDO2 hardware token is resistant to phishing and Man-in-the Middle Attacks.
FIDO and CBA are the 2 authentication protocols recognized as phishing-resistant by cybersecurity regulation bodies such as NIST, ENISA, ANSSI and Dutch cybersecurity agency NCSC ( National Cybersecurity Center).
Based on asymmetric public key cryptography, the FIDO2 security key (USB token or smart card) prevents from phishing because each private key is bound to the domain of the service provider. If the domain is fake, the authentication fails. In addition, all private keys are stored locally and securely in the FIDO2 key which prevent form Man-In-The-Middle attacks.
Yes, the FIDO2 tokens embrace the protection of personal data based on public key cryptography. FIDO2 meets the requirements of the US administration and the EU security agencies for strong MFA. Hardware FIDO security keys are evaluated AAL3 by NIST (Assurance Level 3 , the highest level of Assurance in Authentication according to NIST).