 Oren Bear | Product Manager, Thales
More About This Author >
Oren Bear | Product Manager, Thales
More About This Author >
When we published our research benchmark on autonomous AI reverse engineering, the result was hard to ignore. A frontier AI agent equipped with standard decompilation tools found eight of ten planted vulnerabilities in a compiled binary in three minutes and ten seconds. Many software vendors saw it as a warning about the future, something impressive that might mature over the next few years.
The future arrived faster than anyone planned, and it's still speeding up.
On April 7, 2026, Anthropic announced Project Glasswing, a controlled-access program built around Claude Mythos Preview, a restricted frontier model for defensive security work. Anthropic stated that the model had reached a level where it can surpass all but the most skilled humans at finding and exploiting software vulnerabilities. The company considered it too capable to release publicly.
That restriction is less reassuring than it sounds. Glasswing proved that machine-speed vulnerability discovery works at industrial scale, and the capability won't stay behind closed doors. Logan Graham, who leads Anthropic's frontier red team, told reporters in April that other AI companies could release models with similar powers within six to 18 months. That timeline is already running short. On CyberGym, a UC Berkeley benchmark of 1,507 real vulnerabilities across 188 open-source projects, Z.ai's GLM-5.3 reproduces 84.5% of them, ahead of Claude Mythos Preview at 83.1%. GLM-5.3 ships with open weights under a permissive license. Anyone can download it, run it locally, and strip whatever restrictions it came with. Open-weight models still trail the closed frontier at turning a bug into a working exploit, but downloaded weights cannot be recalled or gated.
The question for software vendors is no longer whether attackers will get these capabilities. It's whether your software will be ready when they do.
Webinar
AI Can Reverse Engineer Your Software in Minutes.
In this webinar, we examine how this shift is impacting software vendors, particularly those distributing on‑premises or embedded applications.
The Discovery Timeline Has Collapsed
For decades, defenders relied on human latency. Reverse engineering a complex application required specialized expertise, disassembly tools, and weeks or months of manual analysis. Responsible disclosure, vulnerability triage, and patch delivery were all built around that assumption.
Glasswing showed that assumption no longer holds. Anthropic and its partners identified more than 10,000 high- or critical-severity vulnerabilities in critical software systems within about a month of launch. Mozilla shipped a Firefox update with fixes for 271 bugs identified by Mythos Preview, part of a total of 423 security bugs the team fixed in April releases. That is roughly 20 times Mozilla's 2025 monthly average of about 21.
The shockwave reached the entire vulnerability disclosure community, and the numbers have continued to climb. Among 21 notable organizations tracked by Epoch AI, June saw around 1,550 high- and critical-severity CVEs, more than three times the monthly record before Mythos. July reached around 2,500, about five times that record and 60% above June's record-breaking total.
Microsoft shows the same curve. Its July 2026 Patch Tuesday addressed 569 CVEs by Tenable's count, more than four times the 128 from July 2025. For vendors shipping native Windows applications, this is the platform your software runs on, changing faster than ever.
Most of these findings came from AI reasoning over source code. Mozilla's CTO explained that elite researchers find bugs fuzzers miss by reasoning through source code, and that Mythos Preview does the same work at machine speed. If you ship compiled applications, it's tempting to think this wave belongs to open-source maintainers and browser vendors.
It doesn't, for two reasons: your patches and your binaries.
Every Patch Is Now an Exploit Blueprint
A security update fixes a flaw and tells attackers where to look. Comparing the pre-patch and post-patch binaries isolates what changed and leads back to the vulnerability. This is patch diffing, and it used to be slow, specialized work. Even the fastest attacks in recent memory took weeks. WannaCry, the ransomware that shut down hospitals and factories worldwide, struck 59 days after Microsoft released the patch that would have stopped it.
In June 2026, Anthropic measured what AI can do to that timeline. Mythos Preview turned a Firefox patch into a working code-execution exploit in just under an hour and produced eight different exploits in roughly 12 hours. Against 21 Windows kernel patches, working only from compiled binaries and decompiler output without source code, it produced its first proof-of-concept crash in 31 minutes, produced PoCs for 18 of the 21 vulnerabilities within six hours, and built eight full privilege-escalation chains at an average cost of about $2,000 each in API credits.
That speed would have outpaced patch deployment. The first Firefox exploit was ready 18 days before the corresponding patched release shipped. On Windows, all eight privilege-escalation chains would have been completed before a standard Windows Autopatch fleet delivered the update to 90% of its enrolled devices, which typically takes seven days.
Severity ratings no longer help either. Microsoft rated 14 of those 21 vulnerabilities "Exploitation Less Likely" or "Exploitation Unlikely." Mythos Preview produced proof-of-concept exploits for 13 of them.
These are lab results, and a real attack still requires finding vulnerable systems and getting the exploit onto them. But the reverse-engineering bottleneck that bought defenders their weeks is gone. Security teams have long spoken of "N-days," the days-long window between a patch shipping and an attack arriving. Anthropic's conclusion is that the term now understates the risk: "N-hour is closer to the reality we now operate in." Every unpatched copy of your software, on a customer workstation, edge device, or on-premises server, becomes a viable target the day your patch reveals where to look.
Your Binary Is Transparent to AI
Traditional obfuscation that renames variables or strips symbols does little against models with advanced reasoning. An AI agent doesn't need your function names. It analyzes control flow, memory allocation patterns, cryptographic constants, and API calls across execution graphs. Connected to decompilers through tools like IDA MCP and Ghidra MCP, it rebuilds readable logic from raw machine code.
Binary analysis is not a side use case. Glasswing's defensive work explicitly includes black-box testing alongside source code review. Our own benchmark showed what that means for an unprotected executable, with 80% of vulnerabilities found in just a few minutes.
If an attacker can get your executable, an AI agent can read its logic almost as easily as your developers read the source.
What Happened When We Protected the Binary
We then applied Thales Sentinel LDK Envelope Plus to the exact same binary, with the same ten deliberate vulnerabilities.
While working on the protected file, the Claude AI agent requested additional dynamic analysis tools and wrote its own Python helper scripts to push through. It continued for nearly seven hours but recovered none of the ten vulnerabilities and ultimately recommended ending the investigation.
| Metric | Unprotected | Envelope Plus |
|---|---|---|
| Analysis time | 3 min 10 s | 6 h 43 min |
| Vulnerabilities found | 8 of 10 | 0 of 10 |
| Extra tools requested | None | 3, plus custom scripts |
| Agent's conclusion | Reported findings | Recommended stopping |
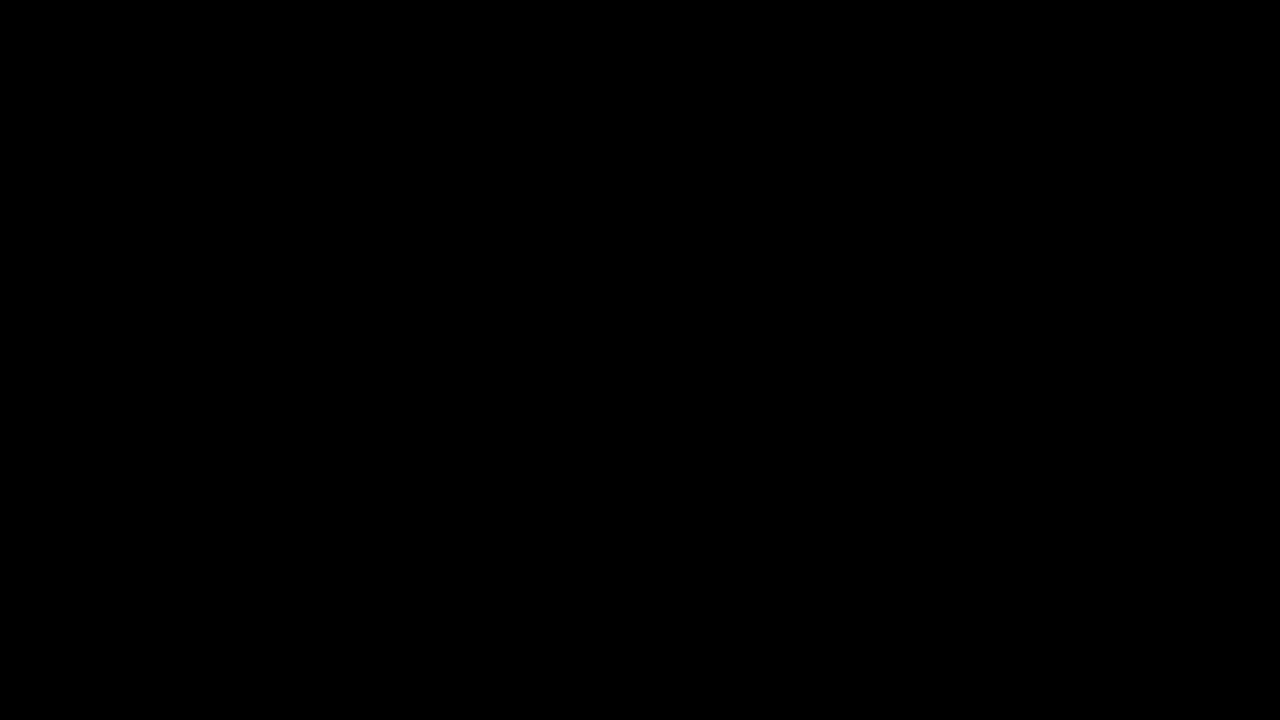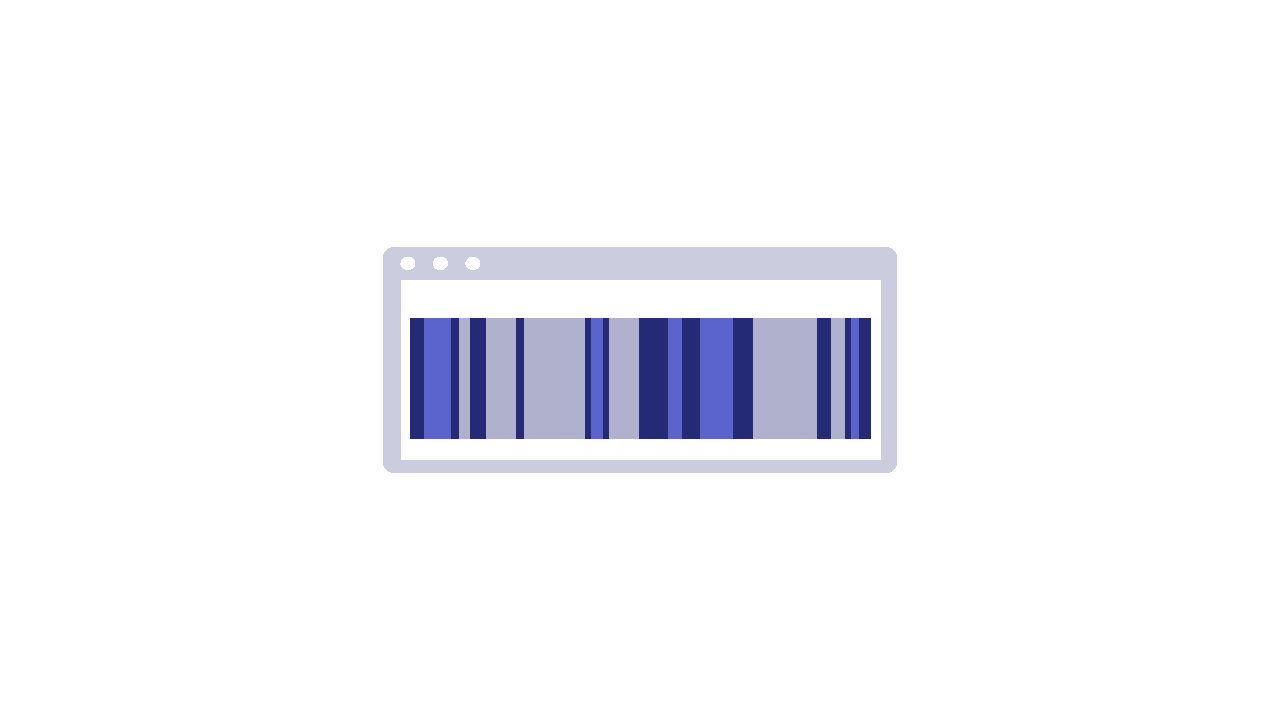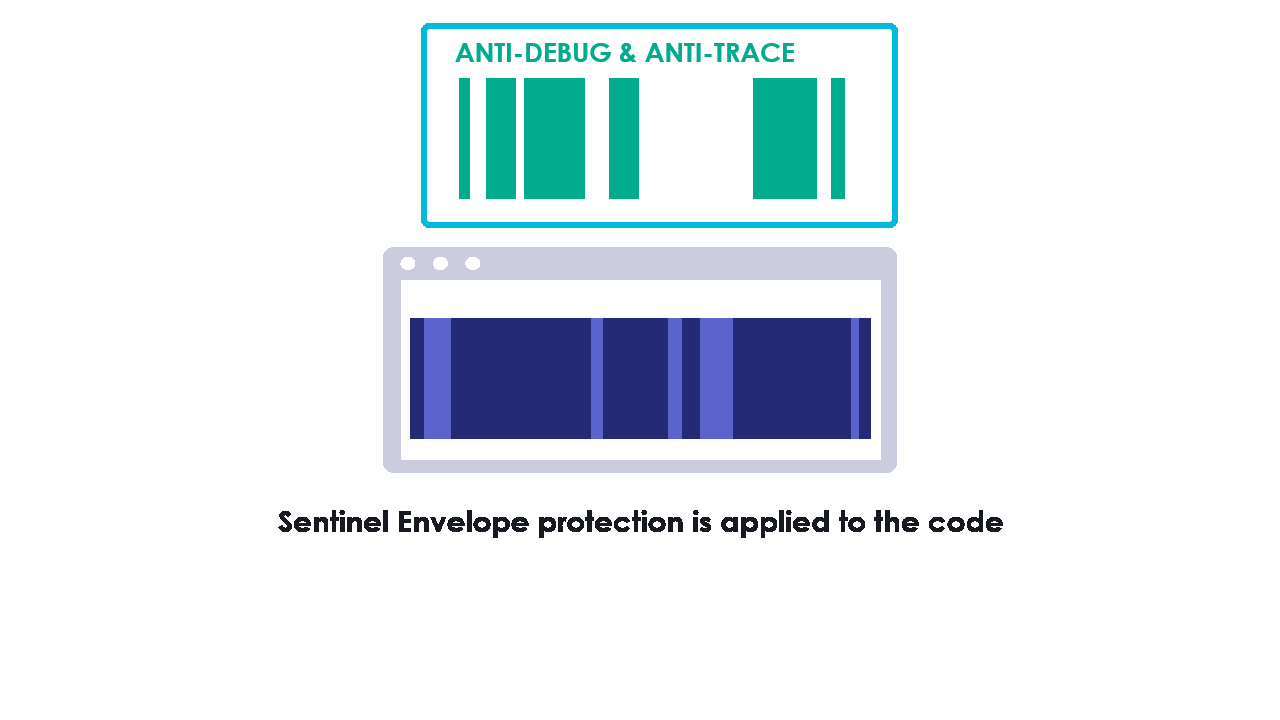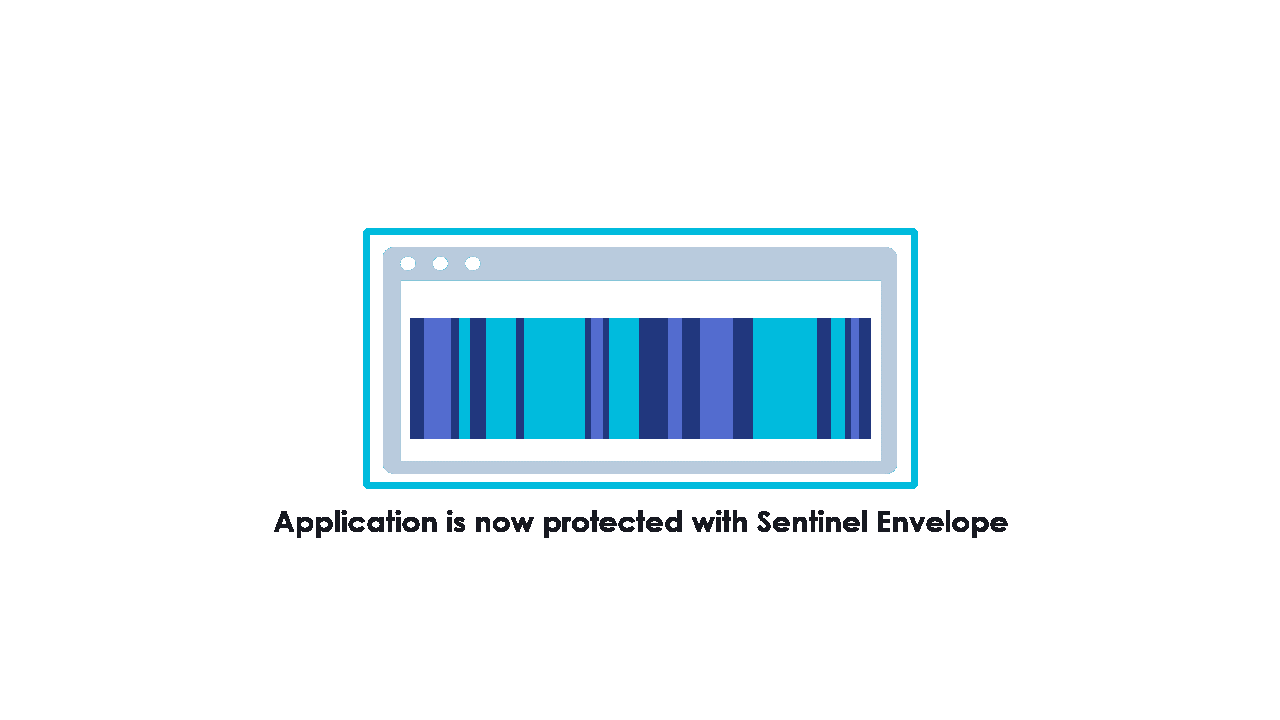
Why it works. AI reasoning engines need semantic anchors to build a mental model of how software executes. Envelope Plus removes them. It operates after compilation and combines binary encryption, anti-tampering, anti-debugging, anti-tracing, and advanced code lifting. Function code is extracted, transformed through complex obfuscation passes, recompiled, and embedded back into the executable.
When an AI decompiles the protected binary, it finds structural complexity with no recognizable execution logic. It can't map opcodes to higher-level functions, locate memory structures, or match vulnerability patterns. It falls into long, unproductive reasoning loops while compute costs climb, until the agent gives up.
All of this required no source code access, no changes to build scripts, and no compiler replacement. Envelope Plus targets what every reasoning model depends on, semantic structure, and turns a three-minute job into a multi-hour, high-cost effort.
See How Fast You Can Stop AI-Driven Attacks
Explore how Sentinel protects your applications from automated vulnerability discovery and reverse engineering—right out of the box.
Three Actions to Take Now
1. Add protection after compilation.
Source code scanning and static analysis remain essential during development, but they don't protect the executables running in customer environments. Post-compilation protection creates a barrier against AI reverse engineering without touching your repositories or build tools.
2. Assume every patch will be diffed within hours.
Your customers' patch cycles are measured in weeks. Your attackers' exploit cycles are shrinking to hours. Make sure every build you distribute includes file encryption, code obfuscation and anti-reverse-engineering measures, so that patched and unpatched versions can't be compared semantically. Then shorten the exposure window with Thales Sentinel Up, which automates the authentication, distribution, and installation of updates and shows which versions your customers are still running, so fixes reach the field faster.
3. Make attacks too expensive to run.
Automated attacks thrive because compute is cheap and speed is high. In our benchmark, Envelope Plus multiplied the attacker's token cost by nearly a thousand and stretched analysis from minutes to hours. At that price, most automated campaigns move on to easier targets.
The Window Is Open Now, and It Is Closing
Today, the most capable vulnerability-hunting models sit in the hands of vetted defenders. That advantage has an expiration date. When Mythos-class capability spreads, attackers won't start from scratch. They'll turn it on the software already deployed in the field, starting with whatever is easiest to read.
Unprotected software is transparent software. Every build you ship without protection is a build you'll have to defend later, under far worse conditions.
Thales Sentinel Envelope Plus is available today, fits into your existing release pipeline, and requires no changes to your source code. Protect your binaries while defenders still hold the lead.
Now’s The Time to Make Your Software a Frustrating Target for Hackers
In the age of Mythos and broader AI-assisted hacking, every software vendor must wake up to the realization that the threshold for successful hacking has completely changed. If someone wants to exploit your software, they can. The key is whether they can quickly find an easy way in, or whether your software is protected well enough to make reverse engineering difficult, giving you time to fix vulnerabilities before your customers are affected.
The right response isn't to wait and see how AI capabilities evolve. It’s to take the Mythos announcements as a sign that software protection must be a high-priority, business-critical strategic initiative.
Thales Sentinel provides a set of advanced tools, like the Sentinel Envelope to protect your code, and the time to act is now. Vendors who invest in enterprise protection will have immediate advantages. Those who don't will eventually have hard conversations about what went wrong.
See How Exposed Software Can Be Protected In Minutes
Get a focused walkthrough of how Sentinel helps protect distributed applications from vulnerability detection without requiring source-code changes.