Protect Linux Data Without Kernel Dependency
Protect sensitive files on Linux servers with transparent encryption, granular access controls, and centralized policy management, while supporting routine patching without kernel-specific agent updates.

Protect Linux Data With Less Operational Complexity
Apply persistent file-level protection while supporting routine Linux patching and centralized security administration.
Protect Sensitive Data
Continuously enforce file-level encryption so protected information remains unreadable to unauthorized users and processes, without requiring changes to applications, infrastructure, system-management tasks, or business practices.
Simplify Linux Patching
Support routine server patching with a UserSpace approach that is agnostic to Linux kernel patches, reducing the need for agent changes tied to kernel updates.

Control Privileged Access
Apply granular policies by user, process, file type, and other parameters to reduce unauthorized access and misuse by privileged administrators.

Centralize Administration
Manage encryption keys and data-access policies centrally with CipherTrust Manager, including key rotation and separation-of-duties support.
Support Compliance Efforts
Encrypt regulated information and track access to protected data and keys to support security, audit, and compliance programs.
Support for CPQ Ciphers
Enables hybrid key exchange using the standard ML-KEM algorithm.
CipherTrust Named an Overall Leader in Data Security Platforms
Thales is proud to have been recognized as an Overall Leader in the KuppingerCole Leadership Compass on Data Security Platforms.
File-Level Encryption Built for Linux
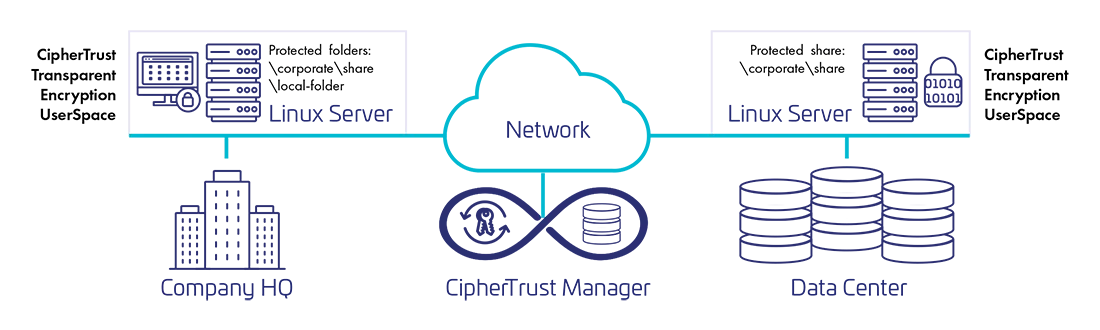
File system-level encryption protects data where it is stored while authorized applications and users continue to work normally. CipherTrust Transparent Encryption UserSpace provides scalable encryption, access control, and data-access auditing for Linux servers, with centralized key and policy management through CipherTrust Manager.
Protect Linux Data Across Changing Environments
Sensitive data is distributed across data centers, big data systems, and public and private clouds. Multiple Linux distributions and frequent operating system updates can make traditional encryption deployments harder to maintain. Thales supports a centralized, policy-driven approach that protects data at the file-system level without requiring application or infrastructure changes, helping organizations maintain protection as Linux environments evolve.
Core Linux Encryption and Access Control Capabilities
Transparent File-Level Encryption
Apply automated file system-level encryption in physical, virtual, and cloud environments. CTE-U encrypts and decrypts data in local and mapped network folders according to policy while authorized applications continue to access files normally.
Common use cases: Data-at-rest protection; Cloud migration; Regulated workloads.
Granular Access Control
Define and enforce policies that control access by user, AI agent, process, file type, and other parameters. These controls help prevent unauthorized access, limit agentic AI actions, and protect sensitive data from misuse by privileged users or autonomous agents.
Common use cases: Privileged-access control; Agentic AI governance; Separation of duties; Insider- and AI-agent-risk reduction.
Kernel-Agnostic Linux Deployment
Use a UserSpace implementation based on Linux FUSE libraries and a single installation package across supported Linux environments. This approach supports ongoing Linux server patching without agent changes tied to kernel updates.
Common use cases: Linux patching; Operating system upgrades; Distributed server fleets.
Centralized Key and Policy Management
Use CipherTrust Manager to centralize encryption keys, access policies, administration, key rotation, and separation of duties for CTE-U deployments.
Common use cases: Key management; Policy administration; Compliance operations.
Data Access Auditing
Create detailed audit logs for activity involving protected files and track access to protected data and encryption keys.
Common use cases: Audit readiness; Security investigations; Compliance reporting.
CipherTrust Transparent Encryption UserSpace
CipherTrust Transparent Encryption UserSpace is a part of the CipherTrust Transparent Encryption suite of products, and provides automated, robust, and scalable file system level encryption for multiple flavors of Linux servers in the distributed enterprise.
What Others are Saying About CipherTrust Data Security Platform
The experience with this has been very good and positive. It is very easy to manage, it also integrates well with our existing infrastructure and has consistently delivered reliable data protection. The deployment process was smooth and the centralized management console made ongoing administration straightforward.”
Vendor is very attentive, offers detailed presales consulting, connects you with other customers, reacts to feedback and questions in a very short timeframe and with competence.”
What I like most about CipherTrust is that it brings all the important data security features into one place. It helps keep sensitive information safe with encryption, manages encryption keys easily, and controls who can access the data. This makes it easier for businesses to protect their information and meet compliance requirements without dealing with multiple tools.”
Gartner and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved.
Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose.
Talk to a Data Security Specialist
Discuss how to protect sensitive Linux data while simplifying patching and administration.
Security that integrates with your technology ecosystem
With one of the industry’s largest cyber security technology ecosystems, Thales solutions integrate with the most widely used technologies to protect and secure access to your mission-critical applications and data.
Related solutions
CipherTrust Transparent Encryption
Explore the broader transparent encryption portfolio and adjacent deployment options.
CipherTrust Manager
Learn how centralized key and policy management supports CTE-U deployments.
CipherTrust Data Security Platform
Explore the platform that brings together data discovery, classification, protection, and centralized management.
Related resources

Frequently asked questions
CipherTrust Transparent Encryption UserSpace, or CTE-U, is a file system-level encryption and access-control solution for Linux servers. It protects files in local and mapped network folders according to centrally managed policies.
UserSpace refers to operating-system code that runs outside the kernel. CTE-U uses this approach to provide encryption without relying on a kernel-specific encryption driver.
No. The product brief states that CTE-U provides encryption and access control without changes to applications or infrastructure.
CTE-U is designed to be agnostic to Linux kernel patches and supports continued server patching without agent changes tied to those kernel updates.
Yes. Policies can restrict access by user, process, file type, and other parameters, including controls designed to prevent privileged administrators from improperly accessing protected data.
CTE-U works with CipherTrust Manager, which centralizes encryption key and policy management for the CipherTrust Data Security Platform.
Examples include payment-card data, personal information, logs, passwords, documents, images, database files, archives, and backups.
CTE-U encrypts sensitive data and provides access controls and audit records that can support requirements involving PCI DSS, HIPAA, and regional data-privacy regulations. The solution should not be described as guaranteeing compliance.